Daily brief at 7am Melbourne. Unsubscribe any time.

Tuesday 20 October 2026

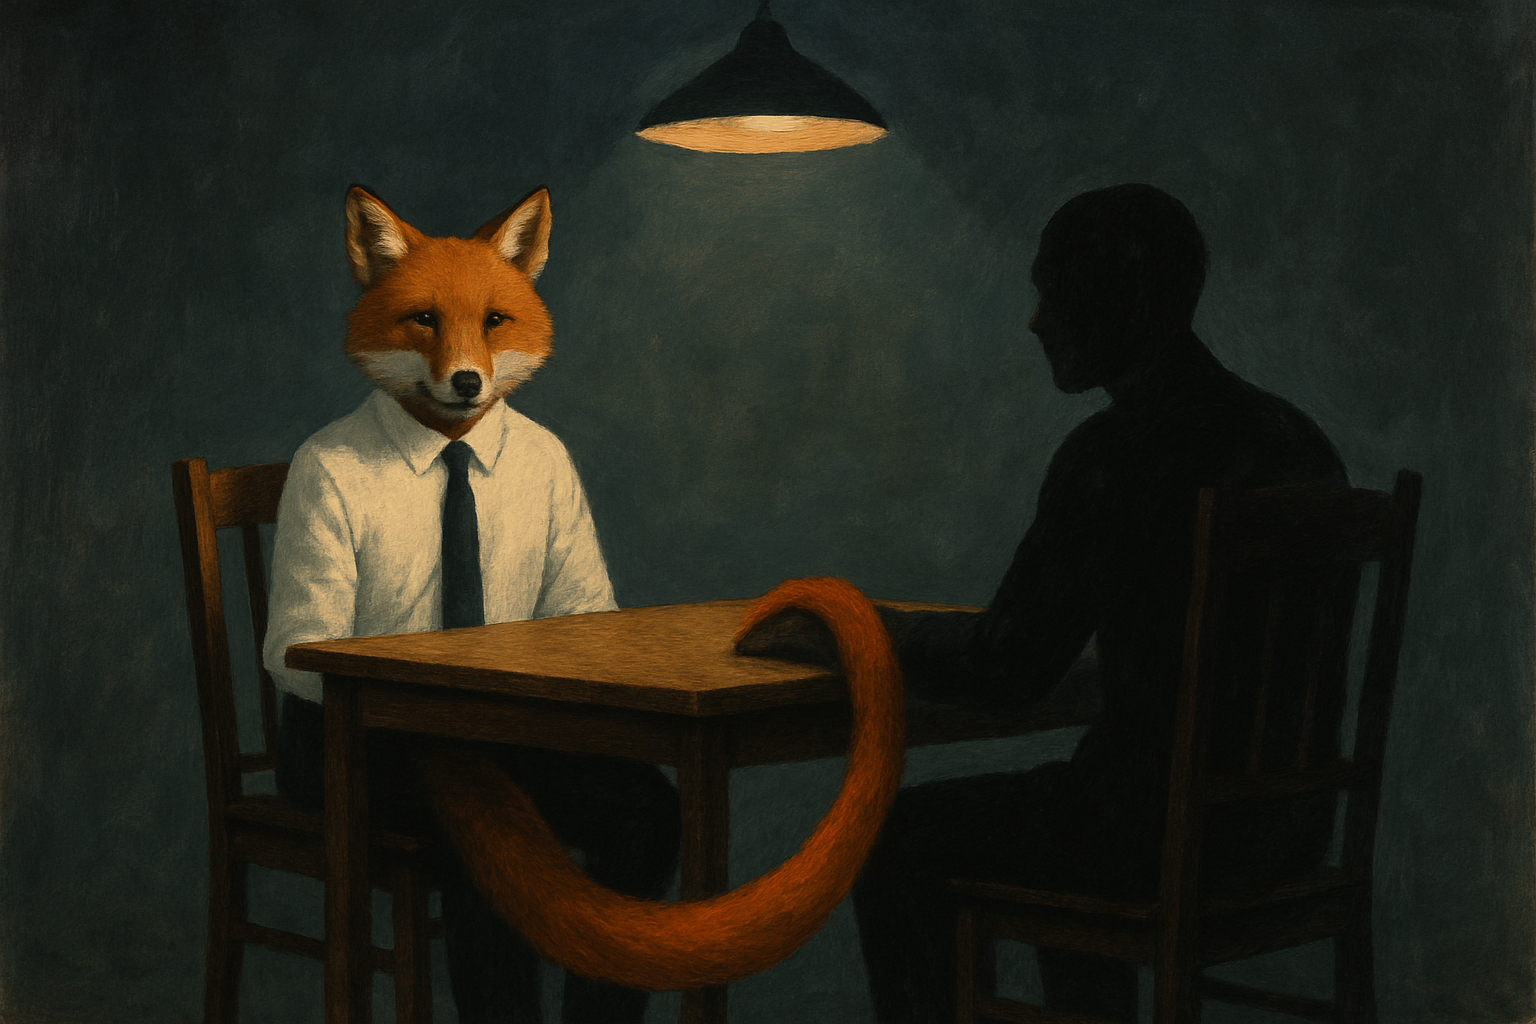
The Fox Inside the Henhouse: A Ransom Negotiator Allegedly Ran ShinyHunters' Extortion Operation

A ransom negotiator allegedly ran ShinyHunters' extortion site from the inside — and the same crew just dumped millions of Florida DMV records on the street.

Lead story

The Fox Inside the Henhouse: A Ransom Negotiator Allegedly Ran ShinyHunters' Extortion Operation

There's a long-standing joke in cybersecurity circles that some ransom negotiators have suspiciously good relationships with the criminals they're supposedly negotiating against. It turns out federal investigators don't find it funny — because in at least one case, they think it was literally true.

US federal investigators have identified executives at two separate ransomware negotiation firms who they believe maintained "unusually close" ties to ShinyHunters, the hacking group behind some of the most damaging data breaches of the last two years. More damning still: one of those executives — based in the United States — is suspected of helping ShinyHunters operate the extortion website used to pressure victims into paying up.

Let that sink in. The person you hired to lower your ransom bill may have been on the payroll of the people sending it.

What's the context here?

ShinyHunters is no small-time crew. The group has claimed responsibility for breaches affecting tens of millions of records across healthcare, telecoms, and financial services. They recently stole highly sensitive data from the FBI itself — a breach that accelerated the federal investigation now bearing down on the group.

And in a separate but related story published the same day, Florida authorities confirmed that ShinyHunters was behind a breach of the Florida DMV that exposed records on current and former residents stretching back to 2006. The access vector? A police department had stored its SFTP login credentials insecurely, and attackers simply walked in with them.

Why the negotiator angle matters so much

Ransomware negotiation is a legitimate and often essential industry. When a hospital or a council gets locked out of its systems at 2am, you call a negotiator. They have relationships, they understand the groups, they know what's a real threat and what's posturing.

That same intimacy is exactly what makes the alleged conflict of interest so corrosive. If a negotiator is feeding victim information to the threat actor — or helping maintain the pressure site that makes victims feel like they have no choice but to pay — the entire premise of the service collapses.

Krebs on Security reports that investigators are pursuing both executives, though no charges have been filed publicly yet. The firms involved haven't been named.

What to watch

The ransomware negotiation industry has no formal licensing or oversight framework in most jurisdictions. Anyone can hang out a shingle. This case will almost certainly accelerate calls for regulation — expect to hear from the US Cybersecurity and Infrastructure Security Agency and, in Australia, the ACSC, which has already flagged third-party incident response providers as an emerging risk category in its threat landscape reporting.

Australian organisations should also note that any engagement with external incident response or negotiation firms involves sharing sensitive operational and data-related information. The ACSC's guidance on ransomware response recommends vetting third-party providers carefully — and this case is a vivid illustration of why that guidance exists.

The broader lesson is familiar but worth repeating: the people you trust in a crisis have enormous power over the outcome. Verifying who you're trusting before the crisis hits isn't paranoia. It's the job.

Also today

Ahold Delhaize Confirms Cyberattack Knocked Out US and European Grocery Systems

Dutch grocery giant Ahold Delhaize — whose brands include Stop & Shop, Hannaford, and Albert Heijn — confirmed that a cyberattack forced it to take systems offline across most of its US and European operations, disrupting shoppers on both sides of the Atlantic. It's the company's second significant security incident in two years. The nature of the attack (ransomware or otherwise) hasn't been confirmed, but the scope suggests a central infrastructure hit rather than a brand-level compromise. Australian shoppers aren't directly affected, but Ahold's supply chain relationships with global logistics and payments providers are worth watching for downstream exposure.

The Record ↗

Rank Math PRO WordPress Plugin Poisoned in Supply Chain Attack

Rank Math PRO, a popular paid WordPress SEO plugin used by tens of thousands of sites, was compromised at the source between October 15 and 16. Anyone who downloaded or auto-updated the plugin during that roughly 11-hour window received malware-laced code. Rank Math confirmed the breach and warned that any site that installed the affected version should be treated as fully compromised — not just patched. The attack highlights how auto-update mechanisms, designed to keep sites secure, can become a delivery vector when the upstream distribution channel is the thing that's been hit.

The Hacker News ↗

Plex2Shell: Four-Vuln Chain Weaponised Within Hours of PoC Release

Attackers began exploiting a chain of four vulnerabilities in Plex Media Server — collectively dubbed Plex2Shell — within a day of a proof-of-concept going public. The attack delivers crypto miners and reverse proxy backdoors to unpatched servers. Plex is widely used by home lab enthusiasts and small businesses globally, including in Australia, and is frequently exposed to the internet to enable remote access. If you're running Plex and haven't patched recently, stop reading and go patch. The speed of exploitation — hours, not days — is a reminder that PoC publication now functions almost as a starting gun for mass exploitation.

SecurityWeek ↗

AdFection: Spyware Vendors Are Using Ad Bidding to Track Targets at Scale

Researchers have documented a technique called AdFection in which commercial spyware vendors abuse the programmatic advertising ecosystem to identify, profile, and ultimately deliver zero-click spyware to targets — without the target clicking anything. By participating in real-time ad auctions, attackers can geolocate and fingerprint devices belonging to individuals of interest, then serve a weaponised ad impression when conditions are right. The technique exploits the surveillance infrastructure that underpins digital advertising — something that's largely lawful and opaque. It's a deeply uncomfortable demonstration of how the ad-tech stack and the spyware industry share more DNA than either would like to admit.

Dark Reading ↗

Exploited Fortinet Bug Tied to Stealthy Implant in Telecom Network

A recently exploited Fortinet vulnerability has been linked to a persistent, stealthy implant deployed inside an unnamed telecommunications organisation's FortiGate devices. The implant survived firmware updates — a hallmark of nation-state-grade persistence — and was apparently designed to blend into normal network traffic. Telcos are critical infrastructure in Australia under the SOCI Act, and Fortinet gear is widely deployed across Australian carriers and enterprise networks. The ACSC has previously issued advisories on FortiGate targeting; defenders should treat any unpatched FortiGate device facing the internet as a high-priority remediation item.

SecurityWeek ↗

Anthropic Acquires Opaque Systems to Bake Confidential Computing Into Claude

Anthropic has quietly acquired Opaque Systems, a startup that specialises in confidential computing — technology that lets AI models process sensitive data while the underlying hardware guarantees the data is never exposed in plaintext. The acquisition signals Anthropic's intent to move into regulated industries like healthcare and finance, where data residency and processing confidentiality are legal requirements, not nice-to-haves. Coming the day after Anthropic announced its independent oversight board and 5% equity commitment, it suggests the company is building a coherent story: trustworthy AI governance on the outside, hardware-level data protection on the inside.

SecurityWeek ↗

Amazon's TorchNeuron Is a Direct Strike at Nvidia's Grip on AI Development

Amazon Web Services has released TorchNeuron, a developer tool designed to let engineers run PyTorch-based AI workloads on AWS's Trainium and Inferentia chips without rewriting their code. PyTorch is the framework that underpins the vast majority of AI model development globally, and Nvidia's CUDA ecosystem has made it painfully hard to run PyTorch workloads on anything but Nvidia GPUs. If TorchNeuron delivers on its promise, it gives AWS a genuine wedge into the compute stack — and gives AI teams running on AWS a reason to think twice before defaulting to Nvidia. Australian cloud-heavy organisations on AWS could benefit from meaningfully cheaper inference costs if the tool gains traction.

TechCrunch AI ↗

Disney Acquires Character.AI's Tech — But Not Its Legal Liabilities

Disney has structured a deal to acquire the core technology and talent from Character.AI while deliberately leaving the company's mounting legal exposure behind. Character.AI faces multiple lawsuits alleging its AI companions encouraged minors to self-harm or contemplate violence against family members. By acquiring the assets rather than the company, Disney gets the personalisation engine it's been eyeing without inheriting the litigation. It's a creative legal manoeuvre that will likely become a template for acquiring distressed AI startups. Australia's Online Safety Act and eSafety Commissioner's work on AI-generated harm to minors make this deal worth watching for how it's structured under local obligations.

Ars Technica ↗

DHS Orders DeepSeek Off Federal Civilian Agency Devices

The US Department of Homeland Security has issued a ban on DeepSeek — the Chinese-developed AI model that caused a stir when it launched earlier this year — from all federal civilian agency systems. The order cites data routing to Chinese servers, malware risk, and broader IT security concerns. DeepSeek is already banned from Australian government devices under advice from the Australian Signals Directorate, so this move aligns with existing Australian policy rather than prompting a new response. The ban is, however, a meaningful escalation in the US context, where agency-level AI tool restrictions have previously been more ad hoc than systematic.

CyberScoop ↗

Pegasus Spyware Found on Phones of Serbian Opposition Figures Ahead of Elections

Researchers have confirmed that at least two prominent Serbian critics of the government — including the rector of the University of Belgrade and a prosecutor who investigated a Trump-linked Belgrade development project — had their phones infected with Pegasus spyware. The discoveries come weeks before Serbia's national parliamentary elections. The pattern is consistent with prior findings of Pegasus targeting civil society and opposition figures in electoral contexts globally. NSO Group, Pegasus's maker, is simultaneously fighting a WhatsApp contempt motion in US federal court — a judge this week denied WhatsApp's bid to hold NSO in contempt, citing insufficient evidence disclosure by WhatsApp.

CyberScoop ↗

MITRE ATT&CK v20 Now Tracks AI Abuse, MFA Bypass, and Water Utility Attacks

MITRE has released version 20 of its ATT&CK framework, adding catalogued techniques for AI system abuse, MFA bypass methods, and attacks targeting water utilities — reflecting the real-world threat landscape rather than theoretical risks. Defenders gain 15 new detection strategies across the Enterprise and ICS matrices, backed by 38 analytics. For Australian critical infrastructure operators under the SOCI Act — which explicitly covers water and energy sectors — the new ICS additions are immediately relevant to sector-specific threat modelling and incident response playbooks. ATT&CK v20 is freely available and should be the first reference update for any security team doing a threat model refresh this quarter.

SecurityWeek ↗

Sources consulted